Research Summary
Target: MrBeast & Chicken Road 2
Research Source: PreCrime™ Labs
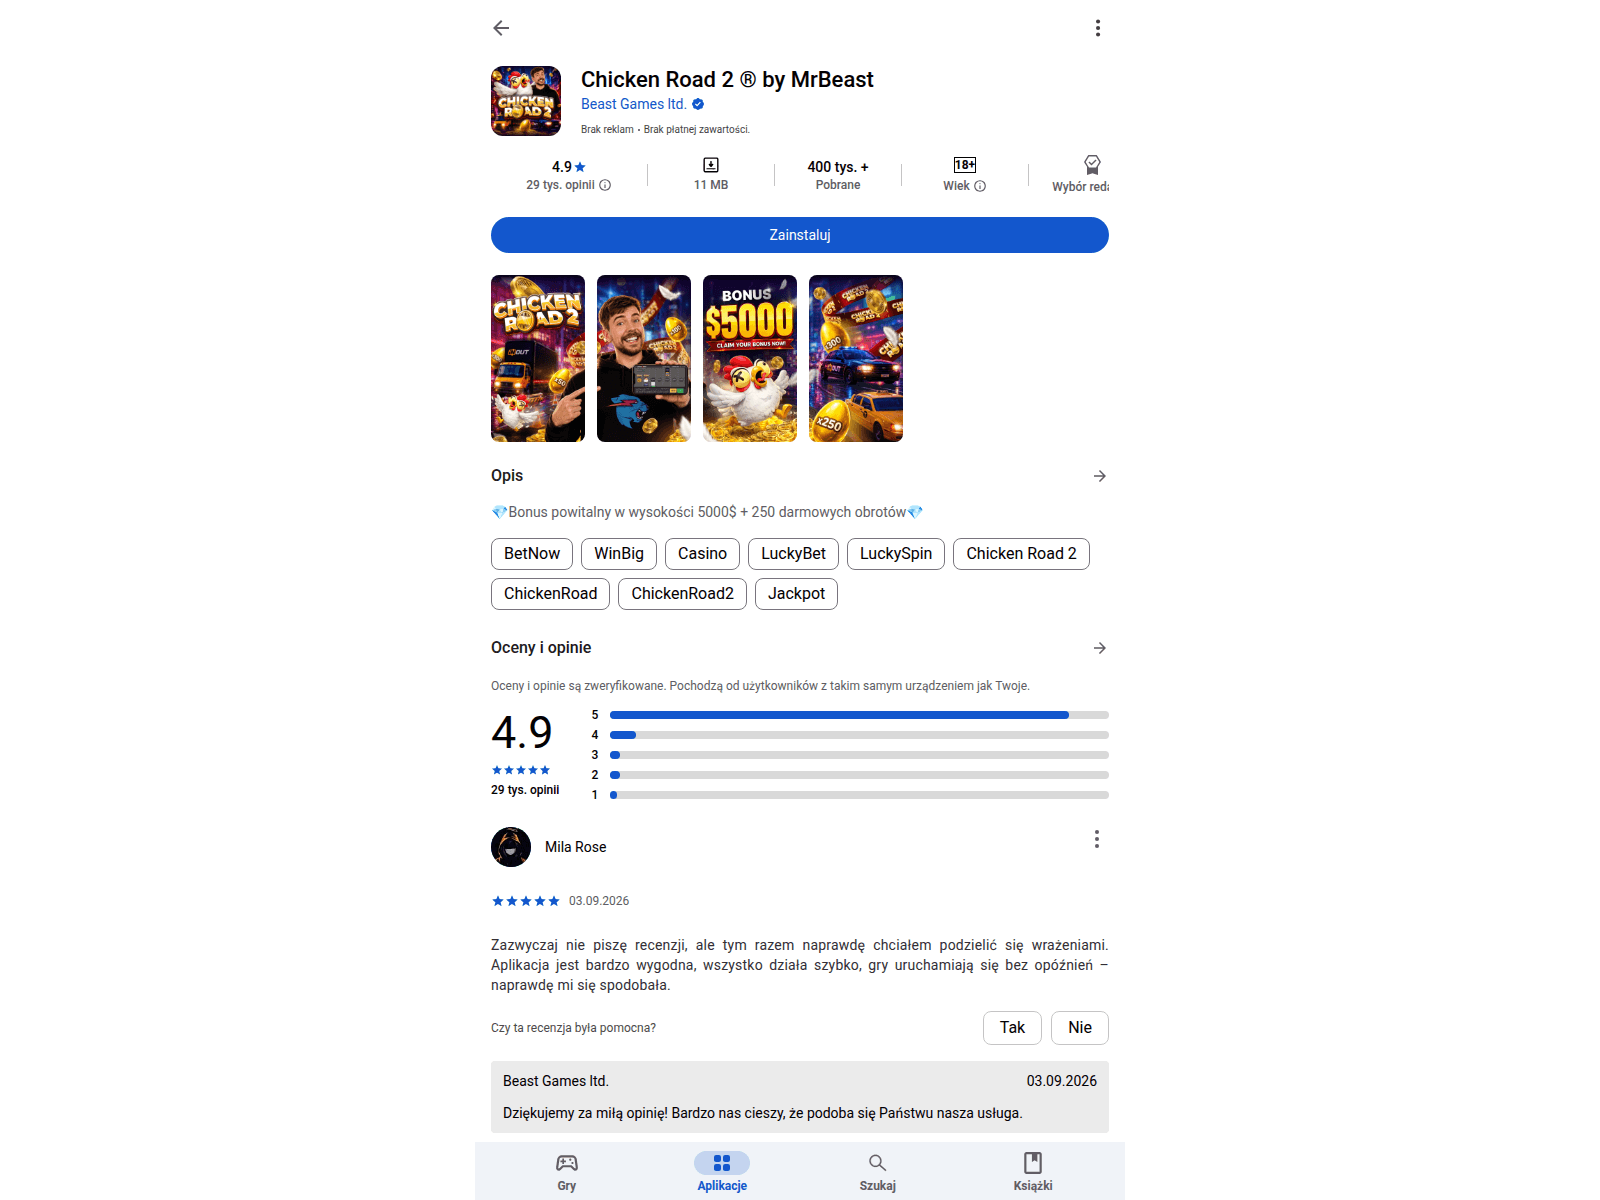
Bfore’s PreCrime Labs observed and uncovered 123 live hostnames (93 apex domains) running one shared Progressive Web App (PWA) “fake app store” kit built to monetize casino affiliate traffic. The kit uses MrBeast, Chicken Road 2, and other game brands as the initial lure and force-redirects the visitor to an affiliate network every 5 seconds. A related Google Play listing, “Chicken Road 2 ® by MrBeast”, uses the same lure with a welcome-bonus pitch of $5000 + 250 free spins.
The research suggests that this is not a set of static clones. Every host serves the same script bundle and PHP endpoints and carries a traffic-distribution (TDS) configuration that separates reviewer-facing “safe pages” from victim-facing “money pages”. The operator is recoverable because a “/config.json” endpoint is readable on every kit and leaks the operator’s TDS account UUID.
The team discovered 86 of 88 parsed configs that share one account, and the activity has run continuously for 14 months (May 2025 – June 2026). A single Firebase project underpins push collection for the whole estate, which makes it a single point of disruption.
Key Indicators (IOCs: Reactive Detection)
Domains / URLs (curated; full list in Appendix):
monsterchickenbst[.]com
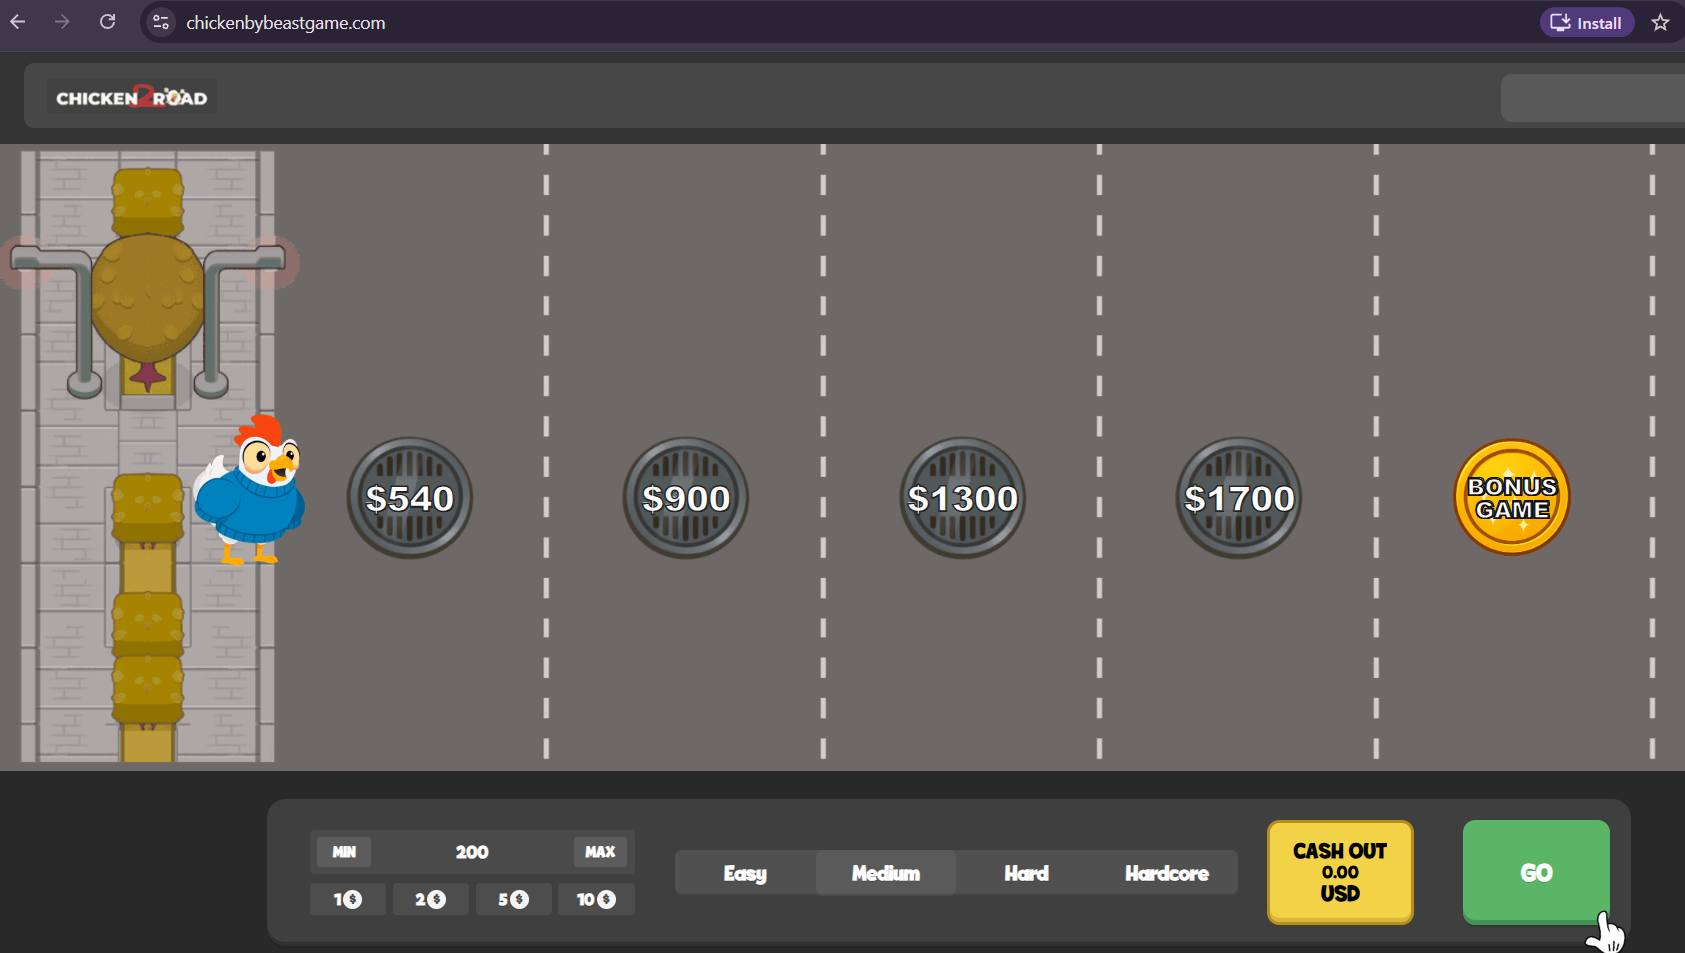
chickenbybeastgame[.]com
Remaining hostnames: supplied in the kit host list (see Appendix, to be attached).
Likely use of evasion or trust abuse with a cloaker serves benign “safe_pages” to reviewers and filtered IPs and the Play listing displays a verified-developer badge and high ratings (4.9, 29K reviews) that are unverified here.
Patterns observed:
Identical kit files on every host: /sw.js?v3, /ua-parser.js?v6, /script.js, /swiper-bundle.min.js, /pagedirect.php, /manifestdirect.php, /pushinstall.php.
Publicly readable /config.json exposing TDS schema fields: money_pages, safe_pages, filter_level, ip_list_mode, stream_id, team_id, click_cost.
Brand-lure hostnames and titles combining “beast”, “chicken”, “road”, “game”, “casino”.
Push-notification permission request followed by FCM token POST to ./pushinstall.php.
Forward Indicators (IOFC – Preemptive Detection)
Identification of domains and pivoting from reactive indicators such as:
Domain structure templates: [celebrity/brand token] + [chicken|road|game|bst|beast] + [game|casino|spin] on .com, e.g. monsterchickenbst[.]com, chickenbybeastgame[.]com.
Keyword clustering: “mrbeast”, “beast”, “bst”, “chicken”, “road”, “chickenroad2”, “betnow”, “winbig”, “luckybet”, “luckyspin”, “jackpot”, “casino” (taken from the Play listing tag set).
Kit fingerprint: any host serving the file set /pagedirect.php + /manifestdirect.php + /pushinstall.php + /config.json with the TDS schema keys.
Additionally, noting the registration cadence across continuous operation over 14 months indicates rolling domain replenishment rather than a single burst. This led by a single Firebase project, one affiliate click endpoint, and two TDS accounts tie the full estate to a single operator.
Accounting into the forward indicators, the newly registered domains (last 30–60 days) should be verified for matching the lure keywords above.
Any new host exposing /config.json with the TDS schema or /pushinstall.php.
Newly published Google Play listings pairing creator/celebrity branding with casino keyword tags and a “Bonus $5000” style pitch, especially around a prominent figure and their latest public announcement.
New TDS account_id values appearing in configs (sign of operator rotation).
Threat Activity Overview
Predictive patterns:
Once the victim lands on a game-branded page (Chicken Road 2 by MrBeast) that behaves like an app store; the push notifications prompts to install, then a 5-second timer force-redirects the visitor to the affiliate network, where casino offers are served. The primary target appears to be mobile and desktop users searching for or likely to serve ads for MrBeast / Chicken Road 2 content. The Play listing is rated 18+ but carries a creator brand with a large young following.
The primary delivery vector is focused on brand-lure domains, with a high clickthrough rate for a Google Play listing impersonating the creator (“Beast Games ltd.”), and subsequent push notifications that re-engage the victim after the initial visit.
There seems to be three monetization pathways for the threat actor from this campaign: per-click and per-conversion payouts from the casino affiliate network,
repeated re-engagement through push notifications,
lure rotation across brands to keep acquisition cost low. “Click_cost” parameter in the config indicates the operator tracks per-click economics.
Impact
Financial exposure: Victims can be steered to real-money casino offers on the strength of a fabricated creator endorsement and bonus claims (“$5000 + 250 free spins”), leading to fraudulent investment under the pretext of quick rewards and being associated with a game led by a popular public figure (MrBeast).
Account compromise risk: No credential theft is observed in the supplied data, the exposure is persistent push access to the victim’s device and downstream casino sign-ups.
Scalability of threat: 123 hostnames from one kit and one Firebase project, the same kit already serves multiple brand lures and can leverage other prominent personalities under the same threat use case seen above.
Likelihood of recurrence: The operation ran 14 months continuously and the kit is brand-agnostic, so takedown of domains alone is unlikely to stop redeployment unless the Firebase project and TDS account are also disrupted. Continuous monitoring and public awareness is recommended.
Recommended Actions
Immediate actions:
Report Firebase project API key and App ID to Google for suspension; this removes push capability across the whole estate.
Submit the Play listing “Chicken Road 2 ® by MrBeast” (Beast Games ltd.) to Google Play for impersonation and gambling-policy review, and notify the MrBeast / Beast brand team.
Pre-block or sinkhole high-confidence matches before they receive traffic. Monitor newly registered domains matching the lure keyword templates and kit file fingerprint.
Public Caution:
The “MrBeast Chicken Road 2” game pages and app listings are not made or endorsed by MrBeast or Beast Games. They are a casino advertising scheme. The page looks like a free game or an app store, then sends you to online casino sites and asks permission to send you notifications. The bonus offers (such as “$5000 + 250 free spins”) are bait. The game is a betting game with real-money stakes.
Recommended measures to avoid being compromised are:
Don’t tap Install, Allow, or Subscribe on it. If the page added an app icon to your home screen, press and hold the icon and uninstall it. Do the same for any “Chicken Road 2 by MrBeast” app you installed from an app store.
Don’t deposit any more money and don’t enter further personal or payment details. Don’t reuse a password from another account on any casino site. Replenish the credentials that were mistakenly reused.
Get games and apps only from the official publisher’s own channels. Check the creator’s verified social accounts before trusting a giveaway or game.
Report suspicious listings with Google Play’s flag option, and report phishing or scam pages to your browser’s safe-browsing reporting tool.
FAQ
Q1: What is this threat?
A casino affiliate scheme that uses MrBeast and Chicken Road 2 branding on 123 hostnames running one shared PWA kit. Visitors are redirected to the Pilots affiliate network every 5 seconds and their push tokens are collected for ongoing notification spam.
Q2: How do we know this is a single operator?
All kit hosts serve identical files, share one Firebase project, and expose a readable “/config.json”. 86 of 88 parsed configs carry the same TDS “account_id”, with a second account on 2 hosts tied to a related casino sub-campaign.
Q3: Are these domains short-lived or persistent?
The operation has run continuously for 14 months with 123 live hostnames, so the estate is persistent and refreshed. Disrupting the shared Firebase project and TDS account is more durable than taking down individual domains.
Appendix: Operator and platform identifiers
| Item | Value |
|---|---|
| TDS account (primary) | dcfe2b81-38de-4ecf-9d4b-b31294e77aa4 (86 of 88 parsed configs) |
| TDS account (secondary) | ba792a44-934c-4eee-a1ee-a12a1e4895cf (2 hosts, Casino de la Vallee) |
| Firebase project / sender | pwa-kit-b2edd / 1073530210274 |
| Firebase API key | AIzaSyAbXMUlcGVnfXhqRuCW3hzcQKMwWS4wEb8 |
| Firebase App ID | 1:1073530210274:web:c2661b73128dd3ad719bbb |
| VAPID public key | BCC8eFqp6UqYc6oA0C3UvUNgvjuN-UNaDP0V--uvQA7otzOS5GO2OMUSe9_GuhKg-qGn82FliegEHVH-6dVB2B4 |
| Operation window | May 2025 – June 2026 (14 months continuous) |